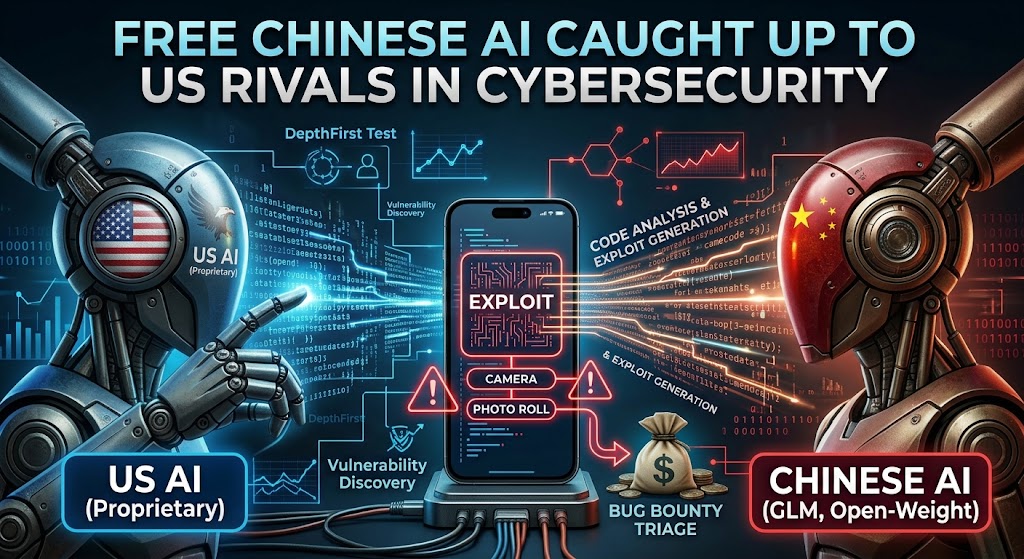
Free Chinese AI Models Catch Up to US Rivals in Cybersecurity
Chinese open‑weight AI models are narrowing the performance gap with their US counterparts, particularly in cybersecurity applications. A recent analysis highlighted how DepthFirst leveraged Z.ai’s GLM model to identify vulnerabilities in TikTok’s open‑source code, demonstrating the growing capability of locally developed large language models to perform sophisticated security testing.
This development underscores a broader shift in the AI landscape, where freely available models from Chinese research labs are increasingly being used for critical tasks like code analysis and threat detection. As these models mature, they challenge the long‑standing dominance of US‑based AI systems in security‑sensitive domains, raising questions about model accessibility, auditability, and the global distribution of AI‑driven cyber‑defense capabilities. The following section details how DepthFirst applied a GLM model to a real‑world target.
How DepthFirst Used a GLM Model to Test TikTok’s Code
Building on the broader trend described above, DepthFirst researchers modified a version of Z.ai’s GLM model to analyze TikTok’s Android application package. By prompting the model to generate exploit code aimed at camera and photo‑roll permissions, they were able to produce a payload that, when executed, granted unauthorized access to these sensitive device functions without user consent.
The vulnerability was reported through TikTok’s bug bounty program, where it remains in the triage phase as of the latest update. This outcome highlights how AI‑assisted code analysis can uncover high‑impact flaws in widely deployed applications, even when traditional testing methods overlook them.
Such demonstrations align with broader trends in AI‑driven security research, where large language models are increasingly used to automate vulnerability discovery—a capability now being explored across industries, from social media platforms to financial systems integrating AI for operational workflows. The key takeaways from this case are summarized below.
Key Facts
- DepthFirst used a modified version of Z.ai’s GLM model to analyze TikTok’s Android application package.
- The model generated exploit code targeting unauthorized access to camera and photo roll permissions.
- The resulting payload could grant access to sensitive device functions without user consent when executed.
- The vulnerability was reported via TikTok’s bug bounty program and remains in triage.
- This case illustrates the growing use of open‑weight AI models in automated vulnerability discovery.
- The test highlights the expanding role of Chinese‑developed LLMs in security‑sensitive code analysis.
DepthFirst GLM security test: Implications for AI Safety and Policy
Reflecting on the findings above, the F5 Labs CASI scoring framework revealed a notable disparity between the security robustness of proprietary and open‑weight models, with the modified GLM used in the test falling into a mid‑range risk category due to its accessibility and limited built‑in safeguards.
This outcome has intensified policy discussions around the release of high‑capacity AI models, particularly regarding whether unrestricted access to model weights lowers the barrier for adversarial use in vulnerability discovery and exploit generation.
Defenders are advised to update threat models to account for AI‑assisted code analysis, implement runtime monitoring for anomalous permission requests, and prioritize patching of identified access control flaws in mobile applications.
Frequently Asked Questions
How does the modified GLM model generate exploit code that targets camera and photo‑roll permissions in an Android app?
The researchers prompt the GLM with a description of the target app and the desired privileged action, causing the model to synthesize code snippets that request those permissions. It then refines the output by iterating on the generated payload until it can programmatically access the camera or photo roll without user consent. The process leverages the model’s trained knowledge of Android APIs and common exploit patterns to produce functional exploit code.
What are the technical limitations of using open‑weight Chinese GLM models for vulnerability discovery compared to proprietary LLMs?
Open‑weight models often lack built‑in safety filters and may produce less precise code, requiring more manual verification by security analysts. Their accessibility also means they fall into a mid‑range risk category, as adversaries can easily replicate the same techniques. Additionally, they may not be updated as frequently with the latest security patches or domain‑specific training data found in proprietary offerings.
What steps can mobile app developers take to defend against AI‑assisted exploit generation like the DepthFirst TikTok test?
Developers should incorporate runtime monitoring that flags unexpected permission requests or anomalous API calls originating from newly installed code. Updating threat models to include AI‑generated payloads and conducting regular AI‑assisted code reviews can help identify hidden vulnerabilities. Finally, promptly patching identified access‑control flaws and employing strict code signing can reduce the attack surface for such exploits.
Last Updated on September 21, 2026 1:05 pm by Laszlo Szabo / NowadAIs | Published on September 21, 2026 by Laszlo Szabo / NowadAIs