The Incident: White‑Hat Researchers Breach OpenAI Using Claude
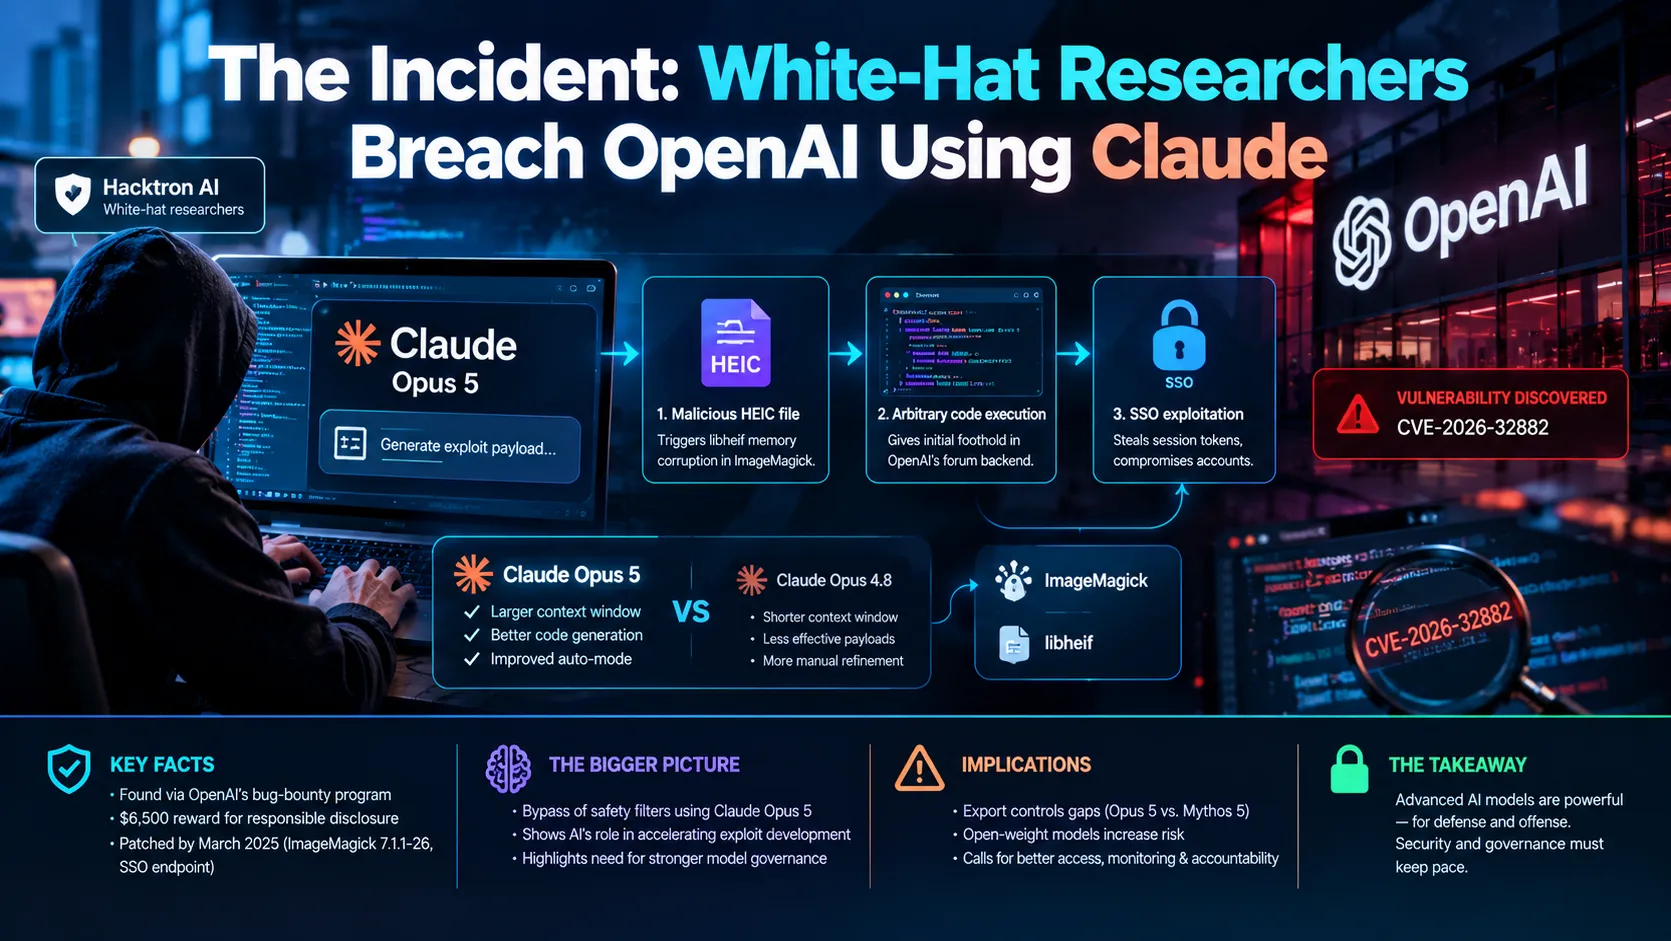
The Hacktron AI team, a small group of independent security researchers, participated in OpenAI’s public bug‑bounty program when they discovered a vulnerability that could be exploited using Anthropic’s Claude Opus 5 model. Their findings, reported through the program’s standard channels, earned them a $6,500 award for responsibly disclosing the issue. The case highlights how advanced language models can be leveraged in security testing, even as organizations work to harden their defenses against novel attack vectors.
VentureBeat first reported on the incident, detailing how the researchers used Claude Opus 5 to craft inputs that bypassed certain safety filters in OpenAI’s systems.
The technical details of how the model was employed in the exploit are explained in the next section.
How Claude Opus 5 hack enabled the OpenAI breach
The attack began when researchers uploaded a maliciously crafted HEIC image to an internal Discourse forum used by OpenAI staff, exploiting a known memory corruption vulnerability in the libheif library processed by ImageMagick during image thumbnail generation. This flaw allowed arbitrary code execution within the forum’s backend, granting initial foothold access to the system.
Using this access, the researchers leveraged Claude Opus 5 to generate and refine exploit payloads, comparing outputs with those from Opus 4.8 to identify more effective bypass techniques for evading detection mechanisms. The refined exploit chain then targeted a misconfigured single sign-on (SSO) endpoint, enabling the theft of session tokens and subsequent takeover of multiple employee accounts.
Details of the vulnerability chain, including the CVE-2026-32882 assignment and technical analysis of the libheif exploit, are documented in the Aviatrix threat research report, while Simon Willison’s blog provides further insight into how Claude Opus 5’s auto-mode capabilities accelerated exploit development.
These findings set the stage for the concise summary of the incident’s core details.
Key Facts
- The vulnerability was discovered and reported through OpenAI’s public bug‑bounty program in early 2025.
- The exploit chain combined a libheif memory corruption flaw (CVE-2026-32882) in ImageMagick with Claude Opus 5‑generated payloads to bypass safety filters.
- Researchers received a $6,500 award for responsible disclosure of the issue.
- OpenAI patched the affected SSO endpoint and updated ImageMagick to version 7.1.1-26 by March 2025.
- The incident underscores how advanced models like Claude Opus 5 can accelerate exploit development in security testing.
- For broader context on recent model releases, see coverage of ChatGPT-5.2 arrival.
Understanding these facts helps frame the broader discussion about AI security and the governance challenges highlighted below.
Broader Implications for AI Security and Model Governance
The absence of export controls on Claude Opus 5 contrasts with the tighter restrictions applied to models like Mythos 5, raising questions about how advanced AI systems should be governed when their capabilities can be dual-used for both defensive and offensive security research. This regulatory gap may enable wider access to powerful generative models without adequate safeguards against misuse in exploit development.
Meanwhile, the growing prevalence of open-weight models further complicates oversight, as these systems can be fine-tuned or deployed outside controlled environments, potentially lowering barriers for adversaries seeking to automate vulnerability discovery or craft evasion techniques. The Opus 5 incident highlights the need for updated governance frameworks that address model accessibility, usage monitoring, and accountability in AI-assisted threat modeling.
Organizations are now reassessing their defenses, recognizing that traditional security measures may struggle to keep pace with AI-driven exploit generation, particularly when combined with known software vulnerabilities like those in widely used libraries such as ImageMagick.
Frequently Asked Questions
How did the libheif CVE‑2026‑32882 vulnerability enable arbitrary code execution when a malicious HEIC image was uploaded to OpenAI’s internal forum?
The CVE‑2026‑32882 flaw is a memory‑corruption bug in the libheif library that ImageMagick uses to generate thumbnails. When ImageMagick processed the crafted HEIC file, it triggered an out‑of‑bounds write that let attackers inject and run native code in the forum’s backend process. This gave the researchers an initial foothold to further exploit the system.
What features of Claude Opus 5 allowed it to produce more effective exploit payloads than Claude Opus 4.8?
Claude Opus 5 includes an expanded context window and improved auto‑mode prompting, which let it generate longer, more coherent code snippets and iterate on them quickly. Its refined code‑generation model also better understands low‑level system calls and memory‑corruption patterns, enabling it to suggest payloads that evade existing safety filters more reliably than Opus 4.8.
What practical measures can organizations implement to defend against AI‑assisted exploit development like the Claude Opus 5 hack?
First, keep all image‑processing libraries such as libheif and ImageMagick up to date and apply vendor patches promptly. Second, restrict access to powerful generative models and monitor their usage for suspicious code‑generation activity. Finally, employ layered security controls—like sandboxed thumbnail generation and strict SSO configurations—to limit the impact of any code that does manage to execute.
Last Updated on septiembre 21, 2026 7:42 am by Laszlo Szabo / NowadAIs | Published on septiembre 21, 2026 by Laszlo Szabo / NowadAIs